CC1101 on an FT232H: a 433 MHz scanner in the terminal · blog.jacq.cc · El Autómata
Lunes, 16 de noviembre de 2026
Portada de las 22:25
Todos los periódicos y la radio, en unoEscrito por IA a partir de Hacker News · Cómo se hace
Hacker News
blog.jacq.cc · texto original
CC1101 on an FT232H: a 433 MHz scanner in the terminal
Six jumper wires from a CC1101 radio module to a CJMCU-232H (FT232H) board, and a Python script on the laptop turns it into a 433 MHz scanner - a spectrum sweep, plus a listen mode that decodes fixed-code remotes. No microcontroller, no soldering, receive only.
Our gate remotes send on 433 MHz and I wanted to see what those signals actually look like. A cheap AliExpress copy remote couldn’t learn them, so I hooked a CC1101 radio module up to a CJMCU-232H - an FT232H board that plugs straight into the laptop. Six jumper wires and a Python script, no microcontroller to flash and nothing to solder.
This setup and test was just to prove that the FTDI board could be connected to the 433 MHz board (bought from AliExpress), and could scan and visualise simple signals from a bootleg remote.
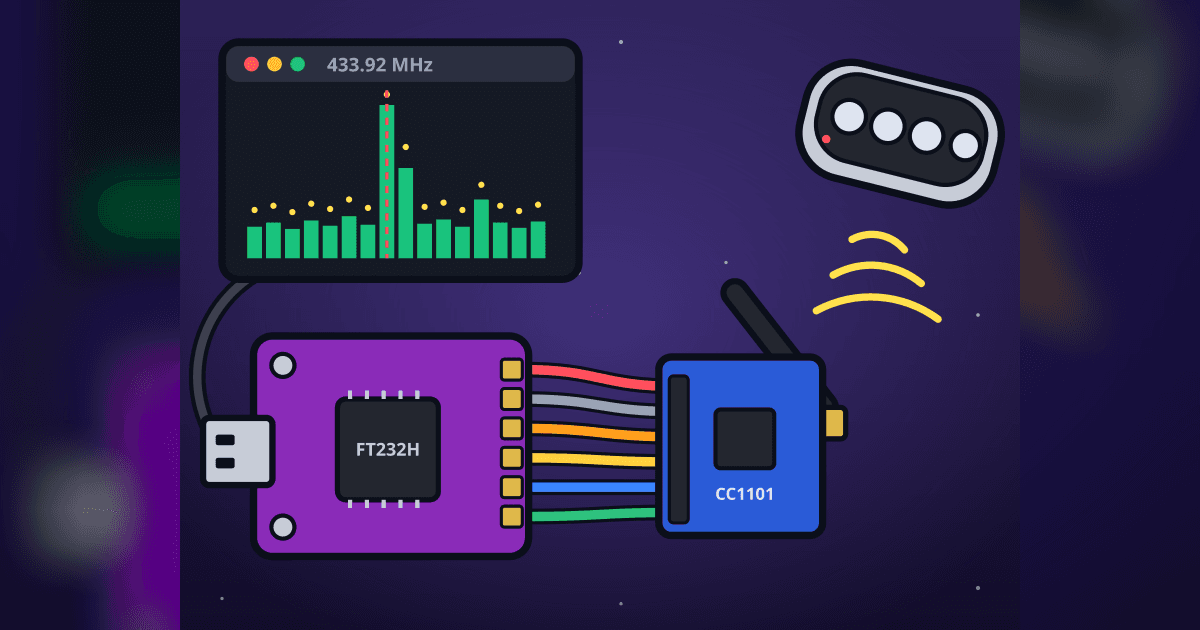
The rig, drawn: the FT232H board, six wires, the CC1101 and its antenna.
A CC1101 433 MHz module and antenna. Mine’s an E07-M1101D (Ebyte’s board layout, with an SMA socket), about AU$3.40 on AliExpress.
A CJMCU-232H - the purple board with an FTDI FT232H chip and a USB-A plug.
A breadboard, 4 male-female jumper wires and 2 female-female.
Something that sends on 433 MHz to test with - I used the copy remote.
The CC1101 talks SPI. A plain USB-serial stick (CP2102, CH340) only does serial, so it can’t drive it. The FT232H does SPI over USB, so Python on the laptop talks to the radio directly. The usual way is an ESP32 running ESPHome, but that means building and flashing firmware every time you change something.
The rule tags the FT232H (USB ID 0403:6014) with uaccess so the logged-in user can open it - no sudo needed to run the scanner. Plug the board in after reloading the rules, or unplug/replug it if it’s already in. --self-test doesn’t need any hardware: it decodes some synthetic noisy presses, plus a real frame from my copy remote.
The CC1101’s header only has pins 1, 2, 7 and 8 printed on it. Pin 1 is the square pad, the odd pins run along the edge of the board and the even pins are on the inside.
CC1101 pin
Name
CJMCU-232H
1
GND
GND on the 4-pin header
2
VCC
+3.3V on the 4-pin header. Never +5V, and not VCORE
4
CSN
AD3
5
SCK
AD0
6
MOSI
AD1
7
MISO / GDO1
AD2
3, 8
GDO0, GDO2
not connected
Six wires. The CJMCU-232H only prints its pin names on the back, so I’ve drawn them in here.
The CJMCU-232H goes on the breadboard, but the CC1101 stays off it - its 2 × 4 header would short its pins in pairs along the breadboard rows. So the signal wires go male end into the breadboard next to the AD pins, and female end onto the CC1101. The power pair goes female to female, straight onto the 4-pin header.
My layout: the board’s AD row sits in rows 21 to 30, with the jumpers in column j next to it.
Screw the antenna onto the CC1101.
Power first, using the female-female wires: CC1101 pin 1 to GND and pin 2 to +3.3V on the 4-pin header.
Signals next, with the male-female wires: pin 4 to AD3, pin 7 to AD2, pin 6 to AD1, pin 5 to AD0.
Leave +5V and CC1101 pins 3 and 8 empty.
Power first: red from pin 2 to +3.3V, brown from pin 1 to GND.
All six wired up. The loose black and orange jumpers aren’t part of it.
The USB plug hangs off the end of the breadboard, so a short USB extension cable helps.
.venv/bin/python rf-scan-ft232h.py
You’ll want a terminal window at least 60 × 20. Before the screen starts, the script checks the radio: it reads the chip’s version (mine says 0x14), writes its settings and reads them back, and checks it’s actually receiving. If something fails it tells you which wires to check. “No CC1101 answers” means power, SCK, MISO or CSN. Settings that read back wrong mean MOSI.
It only receives - it never transmits.
There are two screens, Tab switches between them.
Key
Sweep
Listen
Tab
listen at the marker (Enter too)
back to the sweep
← →
move the marker one column
tune ±10 kHz
[]
move the marker 10 columns
tune ±100 kHz
p
marker to the strongest signal
z
zoom in or out around the marker
b
next band
c
clear
clear
q
quit and print a summary
quit and print a summary
Other options:
--band 315 starts on another band: 433 (the default, 432 to 436 MHz), 315, 300-348, 387-464, 779-928, all, or any START-STOP in MHz.
--listen 433.92 starts on the listen screen.
--text prints plain lines instead of the screen, and --seconds 30 stops it by itself.
--replay /tmp/rf-listen.log decodes a saved log instead of the radio.
The CC1101 only tunes 300 to 348, 387 to 464 and 779 to 928 MHz. With a 433 MHz module and antenna you’ll only hear strong signals in the other bands.
The sweep steps across the band and reads the signal strength (RSSI) at each step. You get bars with peak hold (the yellow dots), a waterfall of past sweeps underneath (newest at the top), and the strongest signals seen along the bottom.
Zoomed out to 402 to 466 MHz, with a remote pressed near 434 MHz.
The 433 band sweeps in 0.16 s. All three bands take 0.6 s.
The noise floor here is about −90 dBm.
Steady signals sit near 408, 416, 418 to 420, 442 and 456 MHz, pressed or not. The one near 416 MHz is the strongest, at about −65 dBm.
A press near 434 MHz reads up to −22 dBm. Close to the antenna it spills into the steps around it, from 431.7 to 436.5 MHz.
On all bands, two more peaks show up at 782 and 883 MHz - both in mobile phone tower bands.
Put the marker on a signal and hit Tab. The listen screen sits on that one frequency and records whatever the CC1101 demodulates. It shows the signal strength over the last minutes, the last frame’s pulses and bits, and every code heard more than once, with a guess at the protocol. The timings go to /tmp/rf-listen.log.
The copy remote. It sends a fixed code - the same bits on every press.
Inside there’s a board marked 520B V2.1: four buttons (K1 to K4), a 433 MHz SAW resonator (R433) and a 12 V 27A battery. The chip is an FMD FT60E021, which is just a general-purpose 8-bit microcontroller rather than a dedicated remote encoder, so the code it sends comes from its firmware. The gate remotes have a KeeLoq encoder chip instead, the HCS300.
The board: the chip (U2), the resonator (X1) and the four buttons.
The chip: an FMD FT60E021 microcontroller.
The back. The antenna is a copper trace printed on the board.
All four buttons of the copy remote, one short press each.
The copy remote sends EV1527-style codes: 24 bits, made up of a 20-bit ID (0x0B80A) and 4 button bits. Its buttons send 0x0B80A1, 0x0B80A2, 0x0B80A4 and 0x0B80A8. The shortest pulse (TE) is 340 µs. The presses came in at −18 to −20 dBm, against a floor of −88 dBm. A remote keeps repeating its code while the button’s down, so each short press gave 3 to 7 frames.
Holding the buttons down fills the list with a bunch of shorter codes too, 12 to 22 bits long, like 0x80A4 and 0x0B80. They’re pieces of the real codes that noise cut short - only the 24-bit rows are real.
Buttons held down: the four real codes, and pieces of them.
The script sets the CC1101 up as an OOK receiver on 433.92 MHz, using Flipper Zero’s AM650 settings: a 650 kHz filter and no packet handling. The chip puts the demodulated data on its GDO1 pin. On this module GDO1 shares a pin with MISO, so while CSN is high nobody’s talking to the chip and MISO carries the data.
The FT232H is already in SPI mode to talk to the radio, and an SPI read clocks bits in at a steady rate. So the script opens a second SPI port on a chip-select pin that isn’t wired, AD4. Reading from it leaves CSN high and clocks MISO in at 50 kHz - a sample every 20 µs, so about 17 of them per 340 µs pulse. A thread keeps the USB reads back to back, and the decoder turns the runs of ones and zeros into pulse lengths.
When the radio’s idle, its output on my rig is mostly high with short dips. That noise often runs straight into the start of a frame and swallows the first bit’s high pulse, so every frame from the copy remote came out 23 bits long instead of 24. The fix was to read that bit from its low pulse alone. In EV1527 a 1 is a long high and a short low, and a 0 is a short high and a long low.
For the sweep, the script tunes to each step, waits 1.2 ms for the chip to calibrate and settle, then reads its RSSI register. The filter is set as wide as the step, so there are no gaps between steps.
The next project builds on this one by now attempting to scan the Richmond remotes, and seeing what they output and what that looks like. They’re the same remotes that open our garage through a GE-RCV1. Inside each one is a Microchip HCS300, a KeeLoq rolling-code chip. A rolling-code remote shouldn’t send the same thing twice. Each press is a 66-bit frame: the remote’s serial number and buttons in the clear, plus a 32-bit encrypted part holding a counter that goes up on every press.
We’ll also attempt to match the signal with known OEM keys (KeeLoq’s manufacturer keys, which each remote’s own key is made from). If a matching key is found I will not be publishing what the key is, but simply that I was able to find it somehow, whether that’s OEM or brute force.
I’m quite excited about this next part of this little experiment, as it’s becoming quite a little sleuthing puzzle to solve.
TI CC1101 datasheet (PDF): the registers, GDO1 on the SO pin while CSN is high, and RSSI to dBm
2 Nov 2026: Step 6: photos of the copy remote's insides, the board and its FT60E021 chip, and a link to its device page with the specs and the full teardown.